Industry Insights
The Supply Chain Is Your Attack Surface
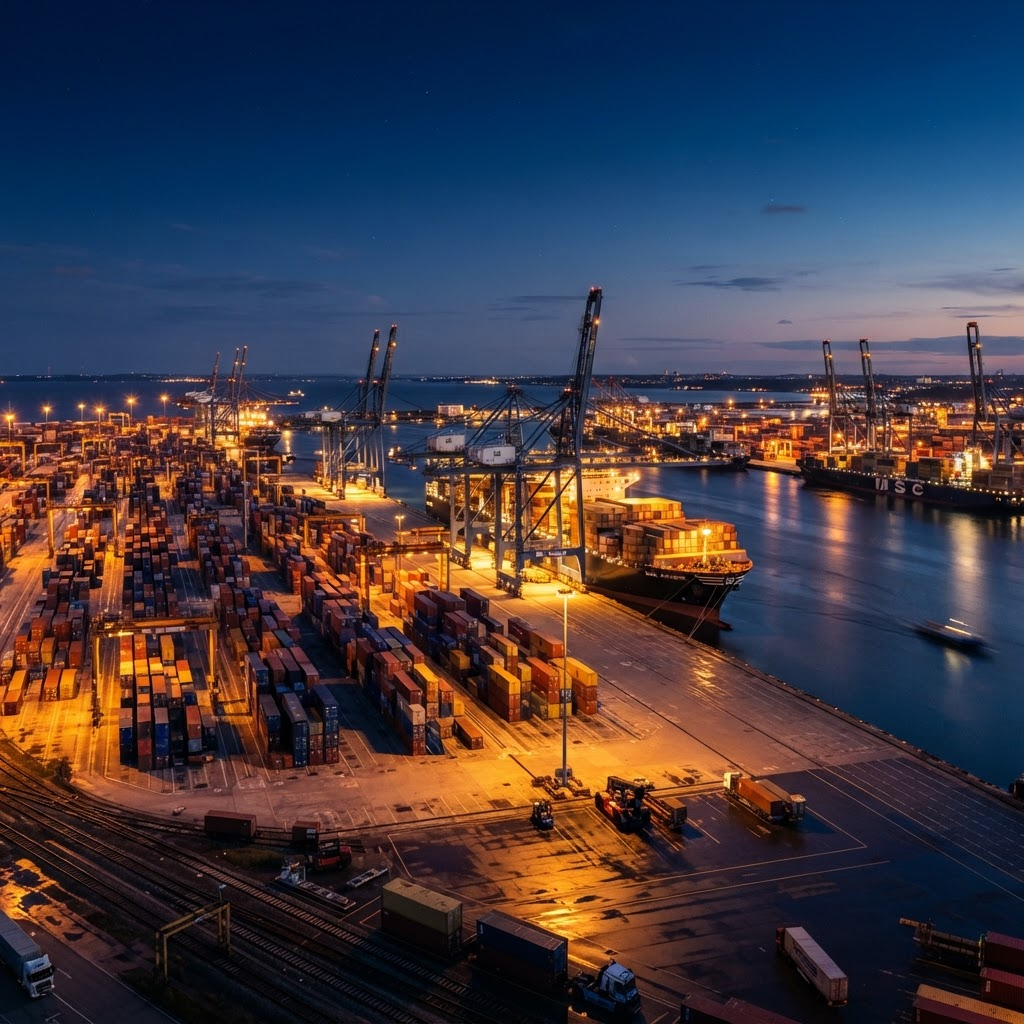
Why supplier due diligence deserves the same rigour as your own security programme — and how to make it proportionate.
Manufacturers and logistics operators have spent a decade optimising supply chains for cost and speed. The result is efficient, tightly coupled networks with very little slack — and remarkably concentrated dependencies that rarely appear on a risk register.
Security teams tend to see supply chain risk as a questionnaire exercise. Operations teams see it as a continuity problem. Both are right, and the two views need to be reconciled in one place.
The reconciliation matters because the two functions maintain different lists. Procurement knows which suppliers carry the most spend; security knows which ones hold credentials; operations knows which ones would halt a line by Thursday. The supplier that matters most is often on only one of those lists, and frequently not the one with the largest contract value.
Concentration is the risk nobody owns
Ask how many of your critical suppliers depend on the same logistics provider, the same cloud region, or the same single-source component. In our assessments, the answer is usually unknown — and the concentration is usually higher than assumed.
Mapping second-tier dependencies for your ten most critical suppliers is unglamorous work that consistently surfaces exposure no questionnaire would have found.
Concentration hides well because procurement measures it in the wrong unit. Three approved suppliers for a component looks like healthy redundancy on a supplier scorecard; if all three ship through the same port, or all three source the same sub-assembly from the same plant, the redundancy is administrative rather than physical. Dual sourcing that converges two tiers down is a single point of failure with better paperwork.
The same pattern appears in software. Four SaaS vendors in the critical path can share one cloud region, one authentication provider, or one payment processor. Diversity at the contract layer tells you very little about diversity at the infrastructure layer, and only the second one keeps operating during an outage.
Make due diligence proportionate
Sending a 200-question security assessment to every supplier produces compliance theatre and little insight. Tier your suppliers by the access and dependency they represent, then apply real scrutiny — evidence, not attestation — to the small group that could genuinely stop your operations.
Access and criticality are different axes and should be assessed separately. A small analytics vendor with a persistent API token into your production data is a security exposure but not a continuity one; a sole-source gearbox manufacturer with no network access at all is the reverse. The office cleaning contractor with out-of-hours building access belongs on the list too, and rarely appears on one drawn up by an IT function.
For the critical tier, ask for artefacts rather than assurances: the scope statement accompanying a certificate, the date and result of their last restoration test, a recent penetration test summary, and the name of the person who would call you during an incident. Certificates confirm that a system was assessed; the scope statement tells you whether it covered the service you actually buy.
For the rest, contractual baselines and monitoring are sufficient and honest.
Write requirements you can enforce
Security clauses that mandate unspecified "industry best practice" are unenforceable. Specify notification timelines, right-to-audit, subcontractor disclosure, and minimum recovery objectives — then verify them at least once for your critical tier.
Notification deadlines deserve particular attention now that regulation has tightened. If you must issue an early warning within 24 hours of becoming aware of a significant incident, a supplier contract permitting them to inform you within five business days makes your own compliance arithmetically impossible. Supplier notification terms need to be shorter than your own regulatory clock, and existing contracts signed before that clock existed are unlikely to satisfy it.
Add the exit case while you have leverage. What happens to your data when the contract ends, in what format, within how many days, and who confirms deletion? Termination assistance is straightforward to negotiate at signature and very expensive to negotiate during a dispute or after a supplier becomes insolvent.
A supplier that cannot commit to a notification timeline has told you something important about their own readiness.
Olha Mann
Founder & Principal Consultant
CISSP · CISM · CEH · ISO/IEC 27001:2022 Lead Auditor